


A new cumulative update has been released for SharePoint 2013 (March 2018 CU)
This CU fixes all SharePoint 2013 products.
SP Build: 15.0.5015.1002
This CU is a full update (Uber package), requiring no earlier updates apart from SP1.
The CU includes all SharePoint 2013 security fixes released since SP1. It does not include SP1, which is required to install this CU.
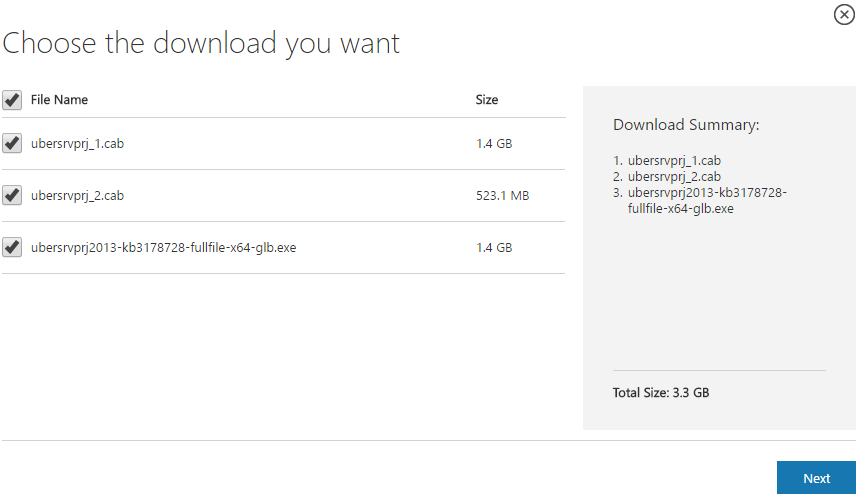
Because of its size, the CU is split into separate CAB files and one executable. Download all these files into the same installation folder before starting the update.
SharePoint 2013 CU – KB articles describing the CU:
- KB 4018299 – SharePoint Foundation 2013 March 2018 CU
- KB 4018302 – SharePoint Server 2013 March 2018 CU
- KB 4018301 – Project Server 2013 March 2018 CU
- KB 4011692 – Office Web Apps Server 2013 in March 2018 CU
SharePoint 2013 CU – CU download link:
- Download SharePoint Foundation 2013 March 2018 CU
- Download SharePoint Server 2013 March 2018 CU
- Download Project Server 2013 March 2018 CU
- Download Office Web Apps Server 2013 March 2018 CU
After installation, remember to run the SharePoint 2013 Products Configuration Wizard, or:
PSConfig.exe -cmd upgrade -inplace b2b -wait -cmd applicationcontent -install -cmd installfeatures -cmd secureresources -cmd services -install
Important
Before installing the CU, ensure SP1 is already installed.
Installation may take up to five hours, so I recommend reading: Speeding up CU and SP installation on SharePoint 2013.
If your farm's patch level is earlier than July 2015 CU, run PSCONFIG immediately after installing the CU to update the schema of certain search databases. More at:
https://blogs.technet.microsoft.com/stefan_gossner/2015/07/15/important-psconfig-is-mandatory-for-july-2015-cu-for-sharepoint-2013
Always install only the CU matching your product version on a SharePoint 2013 farm.
The Project Server 2013 CU already includes:
- CU SharePoint Server 2013
- CU SharePoint Foundation 2013.
The SharePoint Server 2013 CU already includes:
- CU SharePoint Foundation 2013
Remember to update Distributed Cache as well as SharePoint; see How to update Distributed Cache correctly.
Included fixes and improvements
This CU includes the following fixes and improvements.
SharePoint Foundation 2013
This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see Microsoft Common Vulnerabilities and Exposures CVE-2018-0947.
This security update contains improvements and fixes for the following nonsecurity issues:
- Duplicate audit view events are generated when you click on a page from Library view.
- If you are a mobile devices read-only user, you receive an “Access Denied” error message when you access certain features that use third-party scripts.
-
This update addresses an issue that occurs when you set more than 10 indexes on a list and those indexes include a combination of text and non-text based fields.
SharePoint Server 2013
This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see Microsoft Common Vulnerabilities and Exposures CVE-2018-0919 and Microsoft Common Vulnerabilities and Exposures CVE-2018-0922.
This update fixes the following issue:
For files that contain special characters in the worksheet names, you may experience file corruption issue on roundtrip across some locales. Additionally, you may receive the following error message:
Excel found unreadable content in ‘FileName‘. Do you want to recover the contents of this workbook? If you trust the source of this workbook, click Yes.
This security update fixes for the following nonsecurity issues:
- You cannot access a User Profile service application that’s hosted on a SharePoint Server 2016 farm from a SharePoint Server 2013 farm.
This security update also contains the following improvements:
- Provides translation for the setting search loading behavior UI in SharePoint Server 2013.
- Corrects the translation when you follow Hash Tag in the German version of SharePoint Server 2013.
- Improves the indexing compatibility for some malformed PDF files.
Project Server 2013
This security update contains improvements and fixes for the following nonsecurity issues.
- Consider the following scenario:
- You have a Project Web App (PWA) site and Project Server 2013 in your organization.
- You log in to the PWA instance, and then you create an enterprise custom field for the resource entity and another enterprise custom field for the project entity.
- You start Project Professional 2013 and connect to Project Server 2013, add a resource, and set a value to its custom field.
- You save the project and check it in.
- In PWA, you locate the Project Center, drill into the project, and select a Project Details Page (PDP) if you have not already selected one.
- You make a change to the project custom field and then save the project from the PDP.
- In Project Professional 2013, you open the project and view the custom field value.
In this situation, the value of the resource custom field is missing.
- The Manage Queue page may not to be loaded if there is a duplicate Reporting (Project Publish) job. In addition, you may receive the following error message:
Error System.ArgumentException: An item with the same key has already been added.
Office Web Apps Server 2013
This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see Microsoft Common Vulnerabilities and Exposures CVE-2018-0919 and Microsoft Common Vulnerabilities and Exposures CVE-2018-0922.
Komentáře