


A new cumulative update has been released for SharePoint 2013 (October 2017 CU)
This CU fixes all SharePoint 2013 products.
SP Build: 15.0.4971.1001
This CU is a full update (Uber package), requiring no earlier updates apart from SP1.
The CU includes all SharePoint 2013 security fixes released since SP1. It does not include SP1, which is required to install this CU.
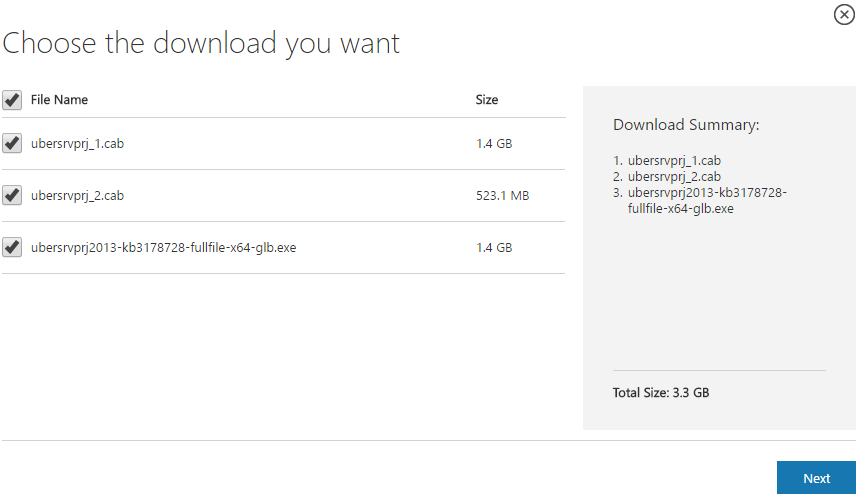
Because of its size, the CU is split into separate CAB files and one executable. Download all these files into the same installation folder before starting the update.
SharePoint 2013 CU – KB articles describing the CU:
- KB 4011173 – SharePoint Foundation 2013 October 2017 CU
- KB 4011177 – SharePoint Server 2013 October 2017 CU
- KB 4011175 – SharePoint Server 2013 with Project Server October 2017 CU
- KB 4011231 – Office Web Apps Server 2013 October 2017 CU
SharePoint 2013 CU – CU download link:
- Download SharePoint Foundation 2013 October 2017 CU
- Download SharePoint Server 2013 October 2017 CU
- Download Project Server 2013 October 2017 CU
- Download Office Web Apps Server 2013 October 2017 CU
After installation, remember to run the SharePoint 2013 Products Configuration Wizard, or:
PSConfig.exe -cmd upgrade -inplace b2b -wait -cmd applicationcontent -install -cmd installfeatures -cmd secureresources -cmd services -install
Important
Before installing the CU, ensure SP1 is already installed.
Installation may take up to five hours, so I recommend reading: Speeding up CU and SP installation on SharePoint 2013.
If your farm's patch level is earlier than July 2015 CU, run PSCONFIG immediately after installing the CU to update the schema of certain search databases. More at:
https://blogs.technet.microsoft.com/stefan_gossner/2015/07/15/important-psconfig-is-mandatory-for-july-2015-cu-for-sharepoint-2013
Always install only the CU matching your product version on a SharePoint 2013 farm.
The Project Server 2013 CU already includes:
- CU SharePoint Server 2013
- CU SharePoint Foundation 2013.
The SharePoint Server 2013 CU already includes:
- CU SharePoint Foundation 2013
Remember to update Distributed Cache as well as SharePoint; see How to update Distributed Cache correctly.
Included fixes and improvements
This CU includes the following fixes and improvements.
SharePoint Foundation 2013
- When you view a list that has more than 1,000 uniquely-secured items, you receive the 0x80131904 exception if there’s a combination of moderation, minor versions, and nondefault draft visibility settings. Meanwhile, the ULS logs display the following information: SharePoint Foundation Database 5586 Critical Unknown SQL Exception 1087 occurred.
- A permission issue may make you unable to access a content type hub after the Hybrid Content Type feature is enabled.
- Add the OneDrive default to cloud feature in hybrid scenarios. After the feature is enabled, you will be redirected to the SharePoint Online OneDrive site when there is any request for the onPrem my site (for example, access SharePoint OneDrive site).
- When Remote Blob Storage (RBS) is enabled, you may be unable to finish downloading a file because of SQL connection pool exhaustion.
- Add term check logic to prevent an odd term that blocks the hybrid taxonomy replication timer jobs.
- Improve the export of versioned list items that are part of a list that has IRM enabled.
- This update translates some terms in multiple languages to make sure that the meaning is accurate.
- This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see Microsoft Common Vulnerabilities and Exposures CVE-2017-11820.
SharePoint Server 2013
- Assume that the administrator is changing the settings of a user profile on the central administration page. After the administrator saves and then reopens the profile, the First day of week and First week of year properties are shifted by one count unexpectedly.
- Improves opaque compound word breaking for the Thai language.
- This security update resolves a vulnerability in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about the vulnerability, see Microsoft Common Vulnerabilities and Exposures CVE-2017-11826.
Project Server 2013
- This update improves the translation of the Task Mode setting name for the Spanish version of Project Server 2013.
Web Apps Server 2013
- This security update resolves a vulnerability in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about the vulnerability, see Microsoft Common Vulnerabilities and Exposures CVE-2017-11826.
Komentáře