


In any secure environment, actively monitor AD DS as part of the overall security strategy. Auditing identifies successful and unsuccessful attempts to modify Active Directory objects, revealing unauthorised logon attempts to computers or network folders.
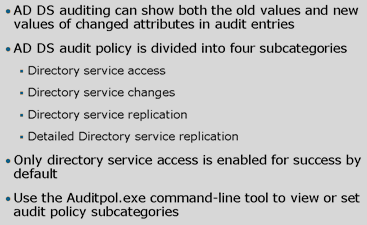
What is AD DS auditing?
Audit logs record attempts to perform specific actions. Enabling auditing on an object or policy shows the actions taken with the user account, date and time.
Auditing has three options:
|
Status |
Description |
| Success (Success) |
An audit entry is logged after the audited action succeeds. |
| Failure (Failure) |
An audit entry is logged after the audited action fails. |
| No Auditing | No audit entry is logged. |
Windows Server 2008 expanded AD auditing from one to four subcategories:
-
Directory service access (enabled by default)
-
Directory service changes (disabled by default)
-
Directory service replication (disabled by default)
-
Detailed Directory service replication (disabled by default)
Auditing event types
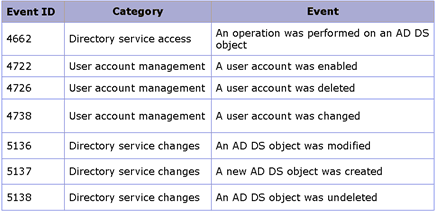
Auditing provides many events; this table lists some of them.
Komentáře