


A new cumulative update has been released for SharePoint 2013 (April 2018 CU)
This CU fixes all SharePoint 2013 products.
SP Build: 15.0.5023.1000
This CU is a full update (Uber package), requiring no earlier updates apart from SP1.
The CU includes all SharePoint 2013 security fixes released since SP1. It does not include SP1, which is required to install this CU.
Because of its size, the CU is split into separate CAB files and one executable. Download all these files into the same installation folder before starting the update.
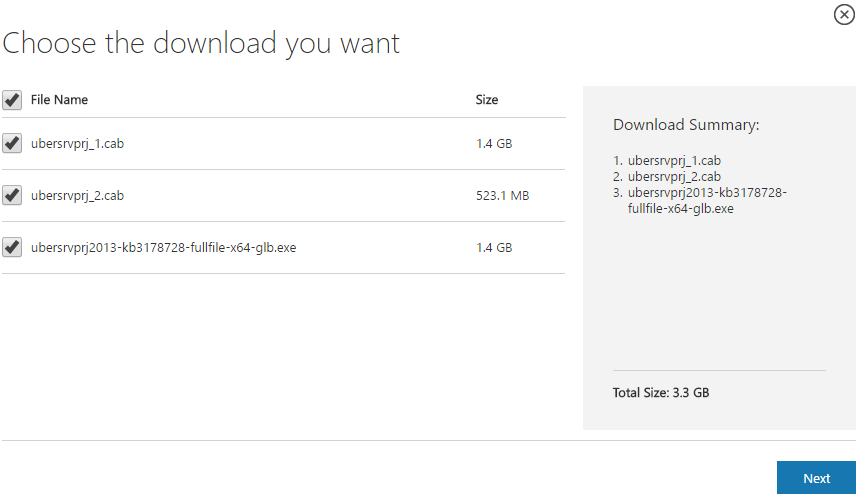
SharePoint 2013 CU – KB articles describing the CU:
- KB 4018345 – SharePoint Foundation 2013 April 2018 CU
- KB 4018348 – SharePoint Server 2013 April 2018 CU
- KB 4018346 – Project Server 2013 April 2018 CU
- KB 4018344 – Office Web Apps Server 2013 in April 2018 CU
SharePoint 2013 CU – CU download link:
- Download SharePoint Foundation 2013 April 2018 CU
- Download SharePoint Server 2013 April 2018 CU
- Download Project Server 2013 April 2018 CU
- Download Office Web Apps Server 2013 April 2018 CU
After installation, remember to run the SharePoint 2013 Products Configuration Wizard, or:
PSConfig.exe -cmd upgrade -inplace b2b -wait -cmd applicationcontent -install -cmd installfeatures -cmd secureresources -cmd services -install
Important
Before installing the CU, ensure SP1 is already installed.
Installation may take up to five hours, so I recommend reading: Speeding up CU and SP installation on SharePoint 2013.
If your farm's patch level is earlier than July 2015 CU, run PSCONFIG immediately after installing the CU to update the schema of certain search databases. More at:
https://blogs.technet.microsoft.com/stefan_gossner/2015/07/15/important-psconfig-is-mandatory-for-july-2015-cu-for-sharepoint-2013
Always install only the CU matching your product version on a SharePoint 2013 farm.
The Project Server 2013 CU already includes:
- CU SharePoint Server 2013
- CU SharePoint Foundation 2013.
The SharePoint Server 2013 CU already includes:
- CU SharePoint Foundation 2013
Remember to update Distributed Cache as well as SharePoint; see How to update Distributed Cache correctly.
Included fixes and improvements
This CU includes the following fixes and improvements.
SharePoint Foundation 2013
This update fixes the following issues:
- The completed check mark column in Task List does not read out by screen reader and does not have the focus indication.
- When a website is deleted, records from Site Version for this website are not removed.
- When you view a calendar item in the Edit Page in SharePoint, you receive an unexpected error message that resembles the following:
Sorry, something went wrong
An unexpected error has occurred.
This update also contains the following improvements:
- Updates the following outdated time zones:
- Central Brazilian Standard Time (UTC-04:00) Cuiaba
- Fiji Standard Time (UTC+12:00) Fiji
- Iran Standard Time (UTC+03:30) Tehran
- Israel Standard Time (UTC+02:00) Jerusalem
- Morocco Standard Time (UTC+00:00) Casablanca
- Pacific SA Standard Time (UTC-04:00) Santiago
- Pacific Standard Time (Mexico) (UTC-08:00) Baja California
- Paraguay Standard Time (UTC-04:00) Asuncion
- Syria Standard Time (UTC+02:00) Damascus
- Changes the retention policy to keep the number of records in the TimerJobHistory table from 10,000 to 3 days.
SharePoint Server 2013
This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see the following Microsoft Common Vulnerabilities and Exposures CVEs:
This update contains the following improvement:
- Provides suitable translation for updated timezone labels.
Project Server 2013
This update fixes the following issue:
When an assignment actual work is missing in a published database, the timesheets page does not load in single entry mode. In addition, you receive the following error message:
The view failed to load. Press OK to reload this view with the default settings. Press Cancel to select another view.
Office Web Apps Server 2013
This security update resolves vulnerabilities in Microsoft Office that could allow remote code execution if a user opens a specially crafted Office file. To learn more about these vulnerabilities, see Microsoft Common Vulnerabilities and Exposures CVE-2018-1028.
Komentáře